

ATLANTA / LONDON — A state-sponsored cyber warfare collective successfully breached the content delivery networks of both CNN and the BBC on Friday, only to discover that not a single human reader could distinguish their weaponized malicious code from the outlets’ regular user experience.
According to federal threat assessment reports, the attackers spent eleven months engineering an intricate JavaScript exploit targeting the third-party web optimization platform Optimizely. The objective was to hijack millions of browser sessions, inject aggressive pop-up banners, and force end users to view relentless propaganda designed to destabilize the Western psyche.
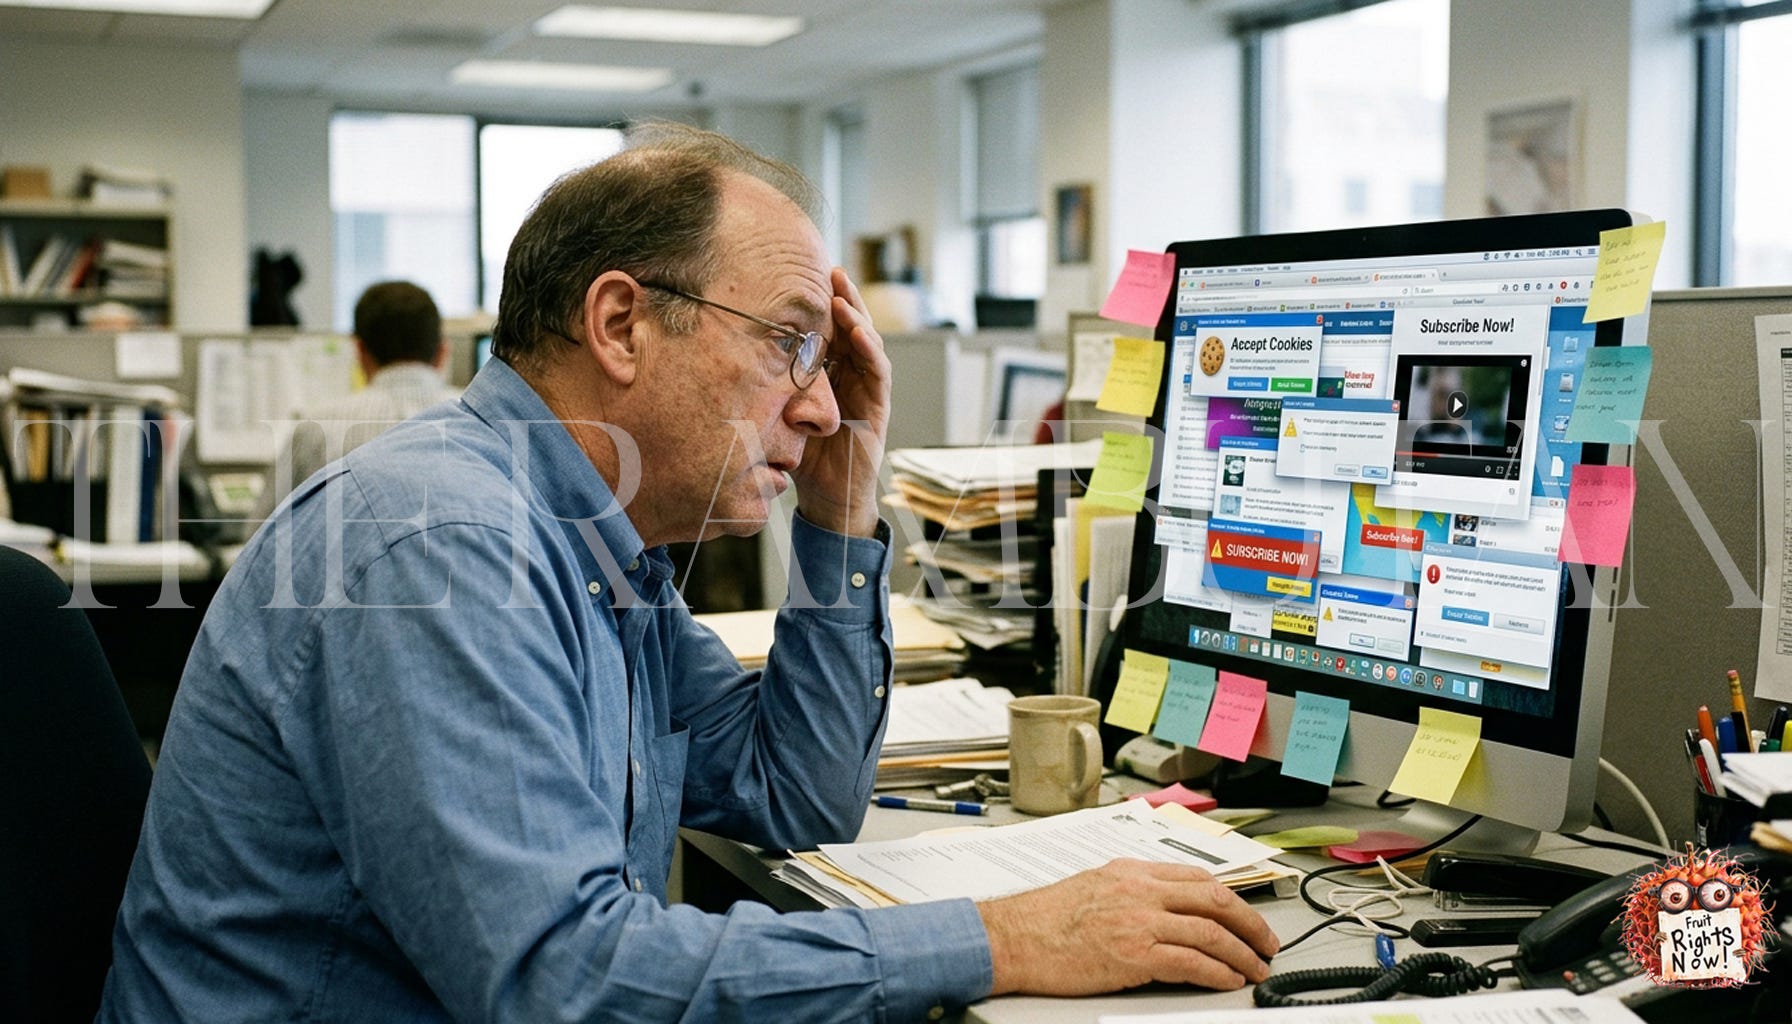
However, upon executing the payload, the destructive malware was swallowed by an impenetrable wall of 74 auto-playing video players, five layers of overlapping cookie-consent agreements, and an ad carousel asking readers if they had what it took to survive the coming collapse of the butter market.
Federal investigators admitted that while the breach was technically catastrophic, its practical impact on the public was functionally zero.
“Unfortunately for the adversaries,” explained Dr. Douglas Vance, Principal Threat Architect at the Cybersecurity and Infrastructure Security Agency (CISA), “they launched it on CNN.com at 2:15 p.m. on a weekday. To the average reader, the malicious payload was indistinguishable from Wolf Blitzer introducing a panel of seven identical think-tank fellows to discuss whether mild drizzle in Des Moines constitutes a threat to democracy.”
According to server logs, the hackers attempted to force user browsers into infinite redirect loops that led to predatory financial scams. Analysts noted, however, that these redirects were quickly crowded out by native Taboola and Outbrain widgets placed directly beneath breaking international news stories, which were directing readers toward headlines such as “12 Celebrities Who Look Unrecognizable In An Open Casket” and “The 3-Second Morning Trick To Obliterate Toxic Belly Sludge.”

Interviews conducted with regular consumers of legacy news revealed that virtually nobody noticed anything out of the ordinary during the twelve hours the exploit was fully active.
“I went on the BBC website to see what the score was in the cricket,” said Nigel Abernathy, a 54-year-old accountant from Surrey. “Suddenly, this giant screen appeared with a red countdown clock, demanding that I surrender my banking details and prove my domestic compliance or face retribution.”
“I naturally assumed it was just the BBC reminding me to pay my TV license,” Abernathy added. “I clicked ‘Remind Me Later’ six times, scrolled past an unskippable thirty-second advertisement for an electric teakettle, and accepted forty tracking cookies. It felt completely normal.”
Across the Atlantic, visitors to CNN experienced similar confusion.
Greg Miller, a hardware store manager in Columbus, Ohio, recounted attempting to look up the weather forecast on CNN’s digital portal when the malware hijacked his audio drivers to play a deafening air-raid siren alongside flashing warnings about systemic institutional failure.
“Honestly, I thought it was just the trailer for Fareed Zakaria’s new weekend special,” Miller said. “It had the exact same production value, and it wouldn’t let me mute it without clicking a tiny grey ‘X’ hidden inside a picture of a mattress sale. I didn’t suspect Russian cyber espionage for a second. If anything, the hacker’s pop-up was less patronizing than Don Lemon used to be.”

By Friday evening, intercepted communications from encrypted dark-web channels suggested that the threat actor syndicate had called off the operation.
Leaked transcripts obtained by cybersecurity researchers revealed that the syndicate’s chief exploit developer broke down in tears after reviewing the operation’s conversion analytics.
“We spent three years studying at elite military academies,” one hacker typed to his commanding officer. “We infiltrated their core directory. We deployed the chaos algorithm. And what happened? Our malware got queued behind an auto-playing video of an egg salad recipe that took 45 seconds to load over fiber-optic internet.”
“One user tried to click our ransomware link,” the hacker continued, “but the screen shifted three inches to the left because an advertisement for toenail fungus treatments finally finished rendering, causing him to accidentally click a slideshow titled ‘You Won’t Believe What the Kid From Jerry Maguire Looks Like Today.’ We didn’t even get his IP address.”
At press time, network executives confirmed they were actively attempting to identify the hacker group to offer them high-paying positions on the digital product team, as their malicious pop-up software was found to load faster than the networks’ existing subscription paywalls.
We write the headlines that haven’t happened yet but probably will. Subscribe to The Rambutan for Southeast Asia’s sharpest fake news.